How to Check the 2023 Secure Boot Certificate Status in Windows 11
Some PCs still use older Secure Boot certificates. Learn how to check the 2023 certificate status and what to do if Windows reports an incomplete update.
- Applies to Windows 11
- 4 min read
- 3 steps
View article illustration
Start with a status check, not a registry change. Windows Security can report whether Secure Boot certificate updates need attention. A PC that boots normally, or merely says Secure Boot is on, has not necessarily demonstrated that its certificate update is complete.
The 2011 certificates are being replaced with 2023 certificates. An incomplete transition can leave future early-boot protections unavailable even while ordinary Windows operation continues. This guide helps you collect the right evidence and choose the supported next step.
Check Windows Security first
- Open Start, search for Windows Security, and open it.
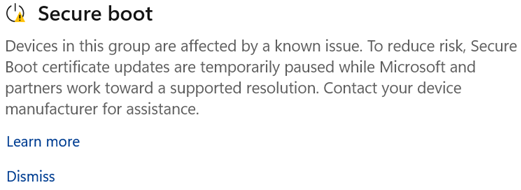
- Select Device security and look for the Secure boot section.
- Read the full message. Record whether it describes completed certificate updates, a pause, a firmware requirement, or unsupported hardware.
If the certificate detail is missing, do not interpret a green icon elsewhere in Windows Security as a certificate result. Record the Windows version/build from winver, install normal supported Windows updates, restart when requested, and check again. A work or school PC should follow its IT team's update process.
| What you find | Next action |
|---|---|
| Certificate updates reported complete | Record the result and date; stop changing settings just to obtain another confirmation. |
| A pause or a hardware/firmware limitation | Check the exact PC model with its manufacturer or IT. A suitable firmware fix might not yet exist. |
| No certificate detail, or conflicting evidence | Collect the build, firmware version and current status before escalation. Missing information is not a success result. |
Step 1: Make sure Windows and firmware are current
Check Settings > Windows Update for updates offered to your supported Windows installation. For firmware, use the PC maker's instructions for your exact model; a similarly named model is not an interchangeable download.
Reading a status value does not need those firmware changes. Keep checking and updating as separate decisions, particularly when the PC is still usable.
Step 2: Check the Secure Boot update status
For an additional read-only check, open Command Prompt and run:
reg query "HKLM\SYSTEM\CurrentControlSet\Control\SecureBoot\Servicing" /v UEFICA2023StatusThis queries a value; it does not create one or start the certificate update. If access is denied on a managed computer, give that result to IT rather than changing permissions.
| Result | Interpretation |
|---|---|
Updated | Windows reports the certificate and boot-manager deployment completed. |
InProgress | Deployment is not yet complete. Check any error information and required restart. |
NotStarted | Deployment has not run; this does not identify why. |
| Key or value not found | This query cannot establish completion. Do not create a value containing “Updated”. |
If a failure needs investigation, the same location can contain UEFICA2023Error. A nonzero value is an error to record. Microsoft advises using UEFICA2023Status, not WindowsUEFICA2023Capable, for general deployment status. The linked registry documentation also contains deployment commands for IT administrators; they are not part of this read-only check.
Step 3: Check Event Viewer if the update is incomplete
Open Event Viewer > Windows Logs > System. Inspect recent TPM-WMI entries and keep the event ID, time and full error code together. Microsoft documents:
- 1795: firmware returned an error while applying a Secure Boot variable update.
- 1801: updated certificates and the boot manager have not been applied to the device firmware.
- 1802: an update was deliberately blocked for a known firmware or hardware condition.
An old failure entry remains in the log after circumstances change. Compare its timestamp with your last update/restart and the current status; repeatedly finding the same old event does not prove a new failure. Do not clear the log just to make the warning disappear.
What should you do if it is not updated?
Send the manufacturer or IT a compact record: exact model, firmware version, Windows build, current Windows Security message, registry result, and recent event details. Keep recovery keys, serial numbers and account details out of public forum screenshots. Ask whether a supported firmware fix or managed deployment is required.
If a supported fix is unavailable, keep Secure Boot enabled and continue normal supported updates while following the manufacturer's guidance. Neither successful startup nor dismissing a notification repairs the certificate state.
Documentation review: 5 October 2026. Checked against the linked official guidance. Screenshots are credited vendor examples, not tests of a reader’s PC. No firmware update or full Windows recovery was performed for this review.
Official references
Microsoft — Secure Boot update impact and diagnosisOfficial reference Microsoft — Windows Security pauses and limitationsOfficial reference Microsoft — Registry deployment-status definitionsOfficial reference Microsoft — Secure Boot event definitionsOfficial reference Microsoft — Find your BitLocker recovery keyOfficial referenceRelated posts
Browse all articles →
Fix Windows Boot Error 0xc0000225 in Windows 10 or 8.1
Troubleshoot boot error 0xc0000225 with Startup Repair first, then repair Boot Configuration Data only when needed.
How to Fix File Explorer Crashes, Freezes, or Won’t Open in Windows 11
File Explorer freezing or refusing to open in Windows 11? Restart Explorer, update Windows, isolate shell extensions, repair system files, and use Windows repair before resetting the PC.
How to Dual Boot Windows and Linux on the Same PC
Prepare a Windows PC for a Windows-and-Linux dual boot, protect your data, handle BitLocker correctly, and use the Linux installer’s supported alongside-Windows option when available.